GAO Report Finds FAA Aircraft Communications Vulnerable to Hacking and Jamming; Agency Accepts Nine Recommendations
Why It MattersThe finding shows that legacy air traffic communications systems, built before modern encryption became standard, remain a structural weak point across the aviation network even as regulators accept remediation plans.
What happened
A Government Accountability Office report released Monday found that communications between air traffic controllers and commercial aircraft are exposed to spoofing, jamming, and interception threats, and that the FAA has not completed the risk assessments or updated the security documentation needed to address them. The report also said the agency lacks real-time detection capability for all spectrum-related threats.
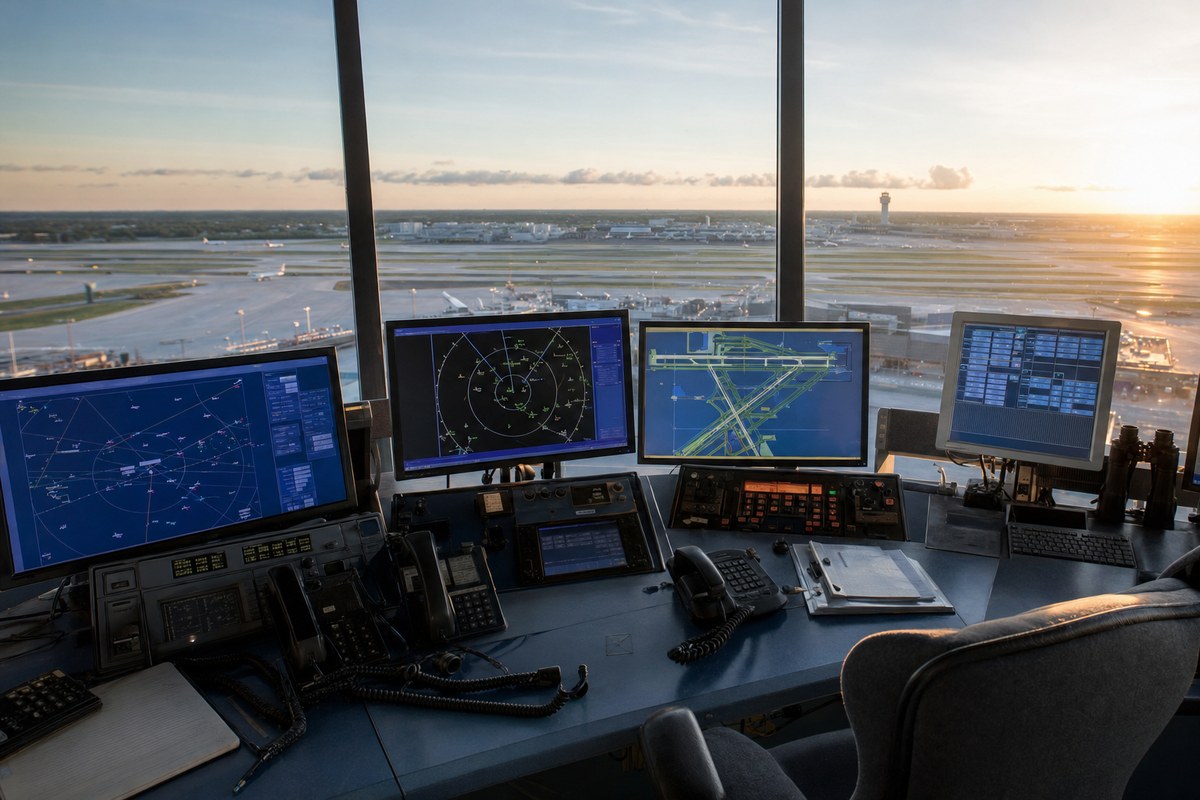
Senator Ron Wyden called the findings "sobering," saying the technology used by air traffic controllers "is incredibly insecure, can be intercepted, impersonated, and jammed, and that hackers and foreign governments can exploit these vulnerabilities to disrupt air travel and even put passengers at risk." He said the FAA's failure to require secure communications represents "a major threat to U.S. national security, to our economy and the safety of the flying public." The GAO report warned that hackers could transmit fraudulent clearance cancellations or other false messages to aircraft, potentially causing flight delays, airspace disruptions, or safety incidents, and said two systems used to send messages to aircraft were developed before modern cybersecurity safeguards became standard practice and lack common encryption protections.
The FAA said it agreed with all nine of the GAO's recommendations, stating: "As aircraft and flight operations become more interconnected, cyber and electromagnetic vulnerabilities pose increasing risks to critical systems, including air traffic control, data communications and avionics." Spoofing and jamming have already caused disruptions in Europe, particularly to satellite navigation systems; Estonia and Finland have attributed GPS jamming in the region's airspace to Russia, allegations Moscow has denied. A 2025 incident involved a Spanish military aircraft carrying the country's defense minister.
Industry impact & what to watch
This case fits into a broader pattern of aviation infrastructure that predates the cybersecurity era being asked to withstand threats it was never designed for. Air traffic communications, navigation and surveillance systems were largely built for reliability against equipment failure, not against a hostile actor deliberately spoofing or jamming a signal, and retrofitting encryption or authentication into decades-old protocols is slower and costlier than building it in from the start.
The segment's exposure runs wider than the FAA's own network. Spoofing and jamming incidents tied to GPS in European airspace, and the case involving a Spanish military aircraft carrying that country's defense minister, show that the vulnerability is not theoretical and is not confined to U.S. airspace. Where attribution has been attempted, as with Estonia and Finland pointing to Russia, the accused state has denied it, leaving the underlying technical weakness as the only settled fact.
What happens next depends on how quickly the nine accepted recommendations move from agreement to completed risk assessments, updated security documentation, and real-time spectrum-threat detection. Congressional oversight, including further statements from lawmakers such as Wyden, is likely to track whether the FAA sets concrete deadlines for closing the two vulnerable messaging systems the GAO identified.